
Detect lateral movement
before it reaches
your crown jewels.
RigetSec unifies threat intelligence, behavioral anomaly detection, and continuous compliance into one autonomous operations console.
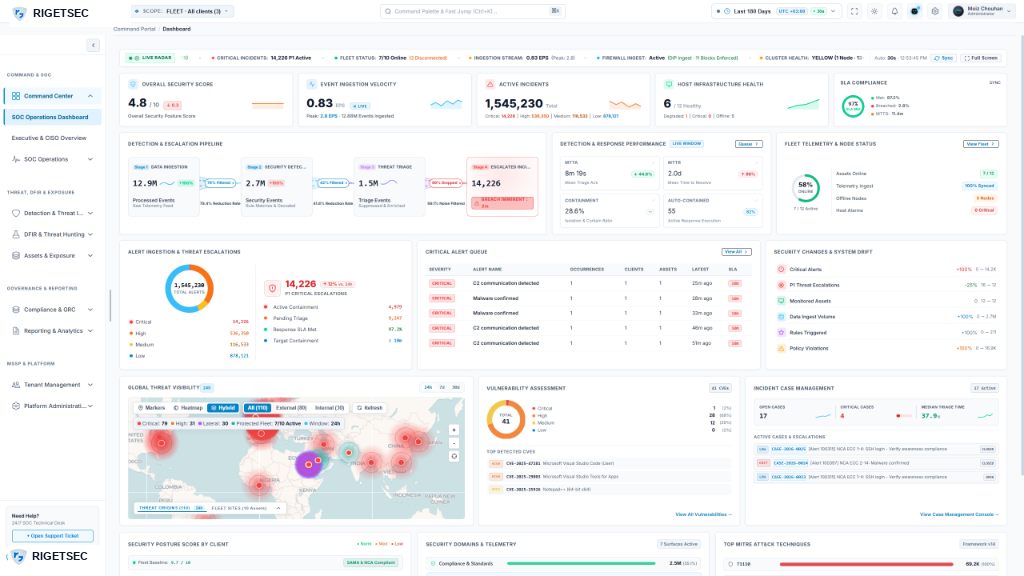
Native ingestion across your existing security fabric
Engineered for Continuous Enterprise Resilience
End-to-end threat detection, automated containment, and audit readiness under one dedicated SLA.
From scattered signals to decisive action.
Unify cloud, identity, endpoint, and network telemetry into one operational picture. Detect what's important, understand the impact, and coordinate response across your security operations.
Platform Capabilities
Autonomous investigation, verified containment, and continuous audit readiness.
24/7 Operations
Managed SOC & MDR
Continuous threat hunting, active host isolation, and verified containment.
Telemetry Hub
Managed SIEM & Logs
High-throughput log ingestion and custom detection engineering.
Machine Speed
Autonomous SOAR
Sub-second alert enrichment and false-positive suppression playbooks.
Adversary Emulation
Offensive Security & VAPT
Certified penetration testing, red teaming, and API security audits.
Governance & Audit
vCISO & Compliance
Executive cyber leadership, pen testing, and turnkey audit readiness.
Machine speed.Human accountability.
The feed is always moving, but the experience stays calm: automated investigation surfaces context, and verified analysts own the action.
Autonomous investigation
Correlate events and suppress noise before it reaches a queue.
SOAR execution stream
LIVE SIMULATED TELEMETRY
Correlated Okta anomalous sign-in with EDR process tree
Approved session revocation playbook for user a.chen
Replayed cloud trail context across 3 affected resources
Containment complete – evidence bundle queued for review
INVESTIGATION TIME
HUMAN-CHECKED
AUDIT READY
From signed contract to first detection in under ten minutes.
Zero complex server agents. Pre-built cloud connectors ingest telemetry securely while machine learning models baseline normal traffic on day one.
Authenticate once. Ingest everything.
Pre-built OAuth flows and IAM roles for AWS, Azure, GCP, Okta, your SIEM and EDR. No agents shipped, no parsers to maintain.
Learn the shape of normal.
Per-identity, per-device, per-segment behavioral norms — zero manual rule tuning. Out-of-profile logins glow in high contrast.
One queue. One console.
Playbooks contain incidents automatically. Posture updates continually. Audit evidence exports are one click away.
Global Threat Intelligence. Local Data Residency.
Guaranteed in-region log residency and regulatory alignment across the GCC and South Asia (NCA-ECC, Qatar NIA, UAE CSC).
API Ingress Exploit & RCE Probe
SSH Credential Stuffing Sweep
Kerberoasting Ticket Extraction
Ransomware Lateral Staging Attempt
Port Sweep & Perimeter Recon
Sanitized telemetry feed · Public IPs anonymized
Multi-Regional Operational Hubs
Serving enterprise and institutional clients across strategic centers in the GCC and South Asia with verified sovereignty, dedicated data residency, and 24/7 response.
Pakistan
South Asia Technology & SOC Hub
Qatar
Middle East Corporate & Advisory Hub
United Arab Emirates
GCC Innovation & Enterprise Gateway
Local presence, sovereign compliance. Our multi-regional hubs ensure native compliance alignment (including Qatar NIA, UAE Cyber Security Council, and regional data residency) coupled with 24/7 command center monitoring and rapid on-the-ground escalation.
Ready to Eliminate Alert Fatigue?
Schedule a confidential architecture review with a Lead Security Engineer.
24/7 SOC architecture review & SLA scoping
SIEM ingestion pipeline and rule tuning assessment
Offensive VAPT and adversary simulation scoping
Sovereign data residency & compliance gap analysis